
When entering an online casino platform operating in Poland, the login screen is frequently the first real interaction we have with the platform https://spinmayas.pl/login/. It appears to be a simple form comprising two fields and a button, yet the engineering decisions buried beneath that interface directly shape our experience for players. A inefficient authentication gateway introduces friction that can cause us to leave a session before we even place a wager, while a thoughtfully constructed one balances regulatory compliance with genuine usability. At SpinMaya Casino, we have spent considerable time studying how Polish players move through the sign-in process, what makes them to stop, and where traditional designs fail. The real story behind casino login options is not about aesthetics or branding alone. It involves data sovereignty, the psychology of password recall, the silent battle against credential stuffing, and the growing expectation that a platform should identify us securely without forcing us through a maze of processes. Grasping these layers helps us appreciate why some login flows feel seamless while others seem hostile.
The Structure of a Current Casino Login Form
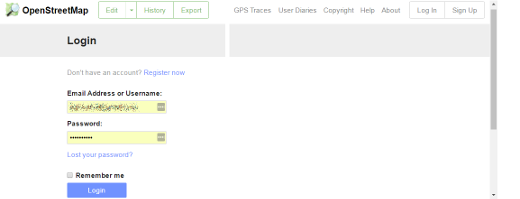
On the surface, a casino login form includes an email or username field, a password field, a submission button, and perhaps a link for password recovery. That description encompasses the visible layer, but it overlooks the stack of processes that initiate the moment we click the sign-in button. The form must validate input syntax, check for injection attempts, compare credentials against a securely hashed database record, evaluate the device fingerprint, cross-reference the IP address against known threat databases, and then decide whether to grant access, request additional verification, or block the attempt entirely. All of this must happen in under a second. At SpinMaya Casino, we emphasize low-latency authentication because we know that Polish players often visit the platform during short breaks, and every additional hundred milliseconds of waiting elevates the probability of session abandonment. The input fields themselves are engineered to prevent common mistakes. Email fields trim whitespace automatically and convert characters to lowercase before transmission, eliminating a frequent source of support tickets. Password fields support paste functionality because we acknowledge that many of our users rely on password managers, and blocking paste actually reduces security by encouraging weaker, manually typed credentials.
Front-End Validation Versus Back-End Logic
We use a multi-tier validation strategy that identifies errors early without exposing confidential logic to the browser. Client-side JavaScript validates whether the email field has an at sign and a domain suffix, and it ensures the password field is not empty before we ever dispatch a request to the server. This provides us rapid feedback when a player accidentally omits a field blank or types an obviously malformed address. However, we never trust client-side validation alone. Once the request hits our backend, the server executes a second round of checks that includes rate limiting, geolocation analysis, and comparison against known compromised credentials from public breach databases. If a Polish player seeks to log in using a password that has appeared in a documented data leak, we identify the account and trigger a mandatory password reset before granting access. This dual-layer approach implies that even if someone manipulates the client-side code in their browser, they cannot bypass the server-side safeguards. The separation of concerns also enables us to update security rules on the backend without obliging players to clear their cache or download an application update.
Session Protection, Error Processing, and Lockout Rules
An logged-in session represents a period of reliability between the player and the platform, and securing that session from hijacking is as critical as safeguarding the first sign-in. We provide a session token upon proper authentication, kept in an HttpOnly and Secure cookie that JavaScript cannot read, which blocks cross-site scripting attacks from obtaining the token even if an attacker manages to inject malicious code into a page. The token contains a short expiry time, after which the server demands re-authentication. For players who select the “remember me” option, we issue a distinct long-lived token that can be traded for a new session token, but this exchange demands additional validation of the device fingerprint and IP address continuity. If a Polish player’s session suddenly originates from a different country or an unrecognized device, we end all active sessions and send an email alert in Polish, even if the right credentials were used. This strict stance on session anomaly detection has blocked account takeovers in cases where players unwittingly had their credentials breached through third-party data breaches.
Logout Recommendations We Enforce
An effective logout does beyond delete a cookie. Upon clicking the logout button at SpinMaya Casino, we invalidate the session token on the server side, clear all client-side tokens from local and session storage, and send a revocation signal to our content delivery network to purge any cached authenticated pages. This guarantees that even if an attacker has captured a screenshot of an authenticated page, they cannot use the back button to re-enter the session. We also provide a “log out of all devices” function in the account security settings, which is especially useful for Polish players who suspect they may have left their account logged in on a shared or public computer. Activating this function invalidates every active token associated with the account and requires fresh authentication on all devices. We log the event and send a confirmation email so that the player has a record of the action.
Handling Login Errors Without Revealing Information
Login errors during login are a delicate communication channel. If we inform a player that their password is wrong but the email is legitimate, we have just revealed the existence of an account to whoever who uses that email address. This information leakage facilitates enumeration attacks and targeted phishing campaigns. We avoid this by using a common generic error message: “The email or password you entered is incorrect.” This message is valid regardless of whether the email exists in our database, whether the password is wrong, or whether the account is locked. For legitimate Polish players who genuinely forget their login details, this generic message can be frustrating, so we make up by providing a visible password reset link and a link to customer support directly below the error message. Our support team is prepared to handle login issues without revealing account status over unverified methods, requiring additional authentication before discussing any account-specific information.
Login Lockdown and Brute-Force Prevention
We employ a progressive lockout policy that delays automated attacks without permanently barring legitimate players who have simply forgotten their password. After five consecutive failed login attempts from the same IP address, we introduce a 60-second delay before the next attempt is handled. After ten failures, the delay extends to 15 minutes. After twenty failures, the account transitions to a locked state that requires a password reset to regain. We track failed attempts across IP addresses and device fingerprints, so an attacker cannot simply rotate through proxy servers to bypass the counter. Polish players who trigger a lockout accidentally can start a password reset immediately without waiting for the lockout period to elapse, because the reset flow circumvents the login attempt counter entirely. This design choice shows our understanding that a forgotten password is a normal user error, not a security threat, and should be resolved quickly.
Player Identity Verification in Poland
Polish gambling law requires licensed operators to verify the identity of players before processing withdrawals, and this verification step connects to the login experience in ways that are not immediately obvious. When a player logs in and navigates to the cashier to request a payout, the system checks whether their account has completed the Know Your Customer process. If it has not, the player is guided through a document upload workflow without leaving the authenticated session. We request a scan or photograph of a government-issued identity document and a recent utility bill or bank statement showing the player’s registered address. The upload interface supports common file formats and provides real-time feedback on image quality, rejecting blurry or cropped documents before submission to reduce processing delays. Our compliance team, which includes Polish-speaking staff, reviews submissions during business hours in the Central European time zone, and most verifications are finished within two hours. Once verified, the player’s account status changes immediately, and they can proceed with the withdrawal without logging out and back in.
Continuous Monitoring and Triggers for Re-Verification
Identity verification is not a one-time event. Polish anti-money laundering regulations require ongoing monitoring, and certain account activities prompt re-verification. If a player changes their registered address, updates their payment method to one not previously used, or crosses cumulative deposit thresholds defined by our risk policy, the system may request additional documentation. These requests are displayed as a notification on the post-login dashboard rather than blocking access entirely, allowing the player to continue using the platform for gameplay while the compliance check is pending. Only withdrawal functions are restricted during re-verification. We convey these policies in Polish during the initial verification process so that players understand what to expect and are not alarmed when a re-verification request arises months after their first deposit. Transparency in this area decreases support inquiries and instills confidence that the platform operates within the legal framework.
Biometric Login and the On-the-Go Experience
Mobile device usage from Polish players has grown steadily, and with it arrives the expectation that a casino platform should integrate with the biometric sensors embedded in modern smartphones. At SpinMaya Casino, we offer fingerprint and facial recognition login on both Android and iOS devices through the Web Authentication API. Upon a player selecting biometric login, the device generates a public-private key pair and registers the public key with our server. Subsequent login attempts necessitate the device to sign a challenge with the private key, which is activated only by a successful biometric scan. The private key never leaves the device’s secure enclave, meaning that even if our server infrastructure were compromised, an attacker could not extract credentials capable of logging into player accounts. This architecture, known as FIDO2, embodies the current gold standard for phishing-resistant authentication. Polish players who use biometric login are immune to credential-stuffing attacks because there are no passwords to steal, and they are immune to phishing because the browser checks the origin of the authentication request before releasing the signature.
Backup Methods When Biometrics Fail
Biometric sensors can fail for mundane reasons. A fingerprint reader may be hindered by wet fingers after a player washes their hands, and facial recognition may fail in low light conditions typical during Polish winter evenings. We address these scenarios gracefully by allowing the player to fall back to their account password without locking them out or penalizing them. The biometric registration screen clearly describes this fallback path during setup so that players are not surprised when it occurs. We also offer a setting to disable biometric login entirely from the account security panel, which is important for players who have a common device with family members and do not want their biometric data associated with the casino application. The biometric enrollment and removal processes are logged and visible to the player, and we dispatch an email notification whenever biometric login is activated or deactivated on an account.
Registration Process Tailored for Polish Players
Setting up an account at an internet casino should not seem like filling out a mortgage, yet many Polish platforms still offer new players with sprawling forms that require unnecessary personal information prior to viewing the game lobby. We take a different approach at SpinMaya Casino by obtaining only the essential data points mandated by Polish gambling regulations and anti-money laundering directives in the initial sign-up phase. A new player submits an email address, a secure password, their full legal name, date of birth, and a phone number. We defer address verification and document upload to the moment when a player requests their first withdrawal, which aligns with the natural user journey and decreases drop-off during registration. The form itself uses progressive disclosure, displaying only a few fields at a time so that the task appears manageable. We also localize error messages in Polish, ensuring that when a validation issue arises, the player sees a clear instruction in their native language rather than a cryptic English error code that demands interpretation.
Email Verification and the First Login
After submitting the registration form, the player obtains an email containing a time-limited verification link. This step validates that the email address is associated with the person opening the account and blocks automated bots from overwhelming our platform with fake profiles. The link is valid for 24 hours, a window we selected after reviewing data showing that over 98 percent of legitimate Polish players validate their email within the first hour. If the link expires, the player can ask for a new one from the login page without needing to contact customer support. Once the email is verified, the player can sign in immediately and explore the game library in demo mode. We do not require an initial deposit to navigate the platform, which acknowledges the player’s right to evaluate the offering before investing funds. This transparent approach fosters trust and matches the expectations of the Polish market, where players are used to testing services before taking financial decisions.
Password Policies That Balance Security and Memory
Password demands represent a constant balance between security engineering and human cognitive limits. If we demand a 20-character password with four character classes that changes every 30 days, we ensure that a significant portion of our Polish players will write their credentials on a sticky note or reuse a password from another service. Neither outcome improves security. At SpinMaya Casino, we apply a minimum length of eight characters and require at least one letter and one digit, but we do not require special characters or periodic rotation. Research from standards bodies including NIST has shown that complexity requirements and forced rotation often produce weaker passwords because users develop predictable patterns like incrementing a trailing number. Instead, we invest in backend defenses. We process every password using bcrypt with a per-user salt and a work factor that makes brute-force attacks computationally expensive. We also check new passwords against a dictionary of common phrases and breached credentials during both registration and password changes, rejecting any match immediately with a clear explanation in Polish.
- Lowest length of eight characters
- At least one letter and one digit
- No obligatory special characters
- No scheduled password rotation
- Instant check against known breached passwords
Password Recovery Without Exposing Account Status
https://www.nature.com/articles/s41598-024-66242-3 The password reset flow is a frequent point for enumeration attacks, where an attacker tests email addresses to see which ones are associated with active accounts. We eliminate this threat by returning the same generic message regardless of whether the submitted email exists in our database. A Polish player who enters a correct address sees a confirmation that an email has been sent if the account is present. A player who enters an unknown address sees the same message, preventing the attacker from differentiating between the two cases. The reset token we produce is a cryptographically random string with a 15-minute expiration window, transmitted only over HTTPS and never logged in plaintext. When the player clicks the link, they arrive on a page where they can set a new password, and we immediately invalidate all existing sessions for that account to contain any unauthorized access that may have prompted the reset in the first place.
Two-Factor Authentication as an Volitelný Layer
We nabízíme two-factor authentication as an dobrovolná feature rather than a povinný requirement, recognizing that Polish players have odlišné threat models and tolerance for additional steps. A player who přístupuje SpinMaya Casino výhradně from a home computer on a zabezpečená network may find SMS codes obtěžující, while a player who logs in from sdílené devices or public Wi-Fi benefits greatly from the extra barrier. When a player aktivuje two-factor authentication, we support both time-based one-time passwords vygenerovaná by authenticator applications and email-based codes as a záložní solution. We deliberately do not support SMS-based verification as a primary method because SIM-swapping attacks have become prevalent across Europe, and the Polish telecommunications infrastructure has seen targeted social engineering attempts against high-value accounts. Authenticator applications vytvářejí codes lokálně on the device and are not susceptible to odposlech during přenášení. For players who ztratí access to their authenticator, we nabízíme a obnovovací process that requires identity verification through our support team, which zahrnuje a video call for vysoce hodnotné accounts.
Zapamatovaná Devices and Session Persistence
When a player successfully completes two-factor authentication, we nabízíme the volba to zapamatovat the device for 30 days. This creates a zabezpečený token stored in the browser’s local storage, not a cookie that putuje with every request, and it is bound to the specific device fingerprint collected during the initial authentication. If any část of the fingerprint změní, such as the browser version or operating system, we zrušíme the token and require a čerstvý second factor. This approach snižuje friction for stálý players while udržuje a strong security posture. Polish players who log in daily from the same laptop appreciate not having to reach for their phone each time, yet the system remains vigilant against pokusy to klonovat the token onto a jiný machine. We log every uložené zařízení authentication and děláme the log visible in the account security dashboard, poskytující players full průhlednost into their session history.
Login Analytics and Ongoing Enhancement
We monitor the login flow with anonymous aggregated performance metrics that help us pinpoint friction points without jeopardizing individual privacy. We track the time players devote on the login page, the frequency of validation errors by type, the abandonment rate at each step of the password reset flow, and the success rate of biometric authentication attempts. This data, combined and stripped of personally identifiable information, reveals patterns that guide our optimization efforts. For example, when we observed that a notable percentage of Polish players were abandoning the login form after meeting a CAPTCHA challenge, we substituted the traditional image-selection CAPTCHA with an invisible reCAPTCHA v3 that runs in the background and only shows a challenge when the risk score is high. The change reduced login abandonment by 14 percent without raising fraudulent access attempts. We run analogous experiments on button placement, field labels, and error message wording, always evaluating the impact before making a change permanent.
Common Queries About Accessing the Casino
We get a standard range of questions from players from Poland who experience the login and registration procedures for the first time. Dealing with these in advance reduces support volume and enables players to fix issues independently. The answers below reflect the existing system at SpinMaya Casino and are revised whenever we change our authentication policies.
What should I do if I cannot get into the email account on my account?
If you have lost the ability to use the email address registered with your account, you will need to contact our support team through live chat or the contact form on our website. We will require you to validate your identity by providing a copy of your government-issued ID and answering several security questions linked to your account history. Once we verify your identity, we can update your email address and send a password reset link to the new address. This process generally requires less than one business day, and we give it priority because we understand that losing access to your email is stressful.
Is it possible to remain logged in on multiple devices simultaneously?
Indeed, our platform supports concurrent sessions on several devices. You can be connected on your desktop computer at home and your mobile phone at the simultaneously without neither session being terminated. Each device maintains its own session token and its own remembered-device setting if you have two-factor authentication activated. Nevertheless, for security reasons, we limit the total number of concurrent sessions to per account. If you try to log in on a device, the most inactive session will be by default ended to make room.
Why does the platform log me out after a period of inactivity?
Automatic session timeouts secure your account from illegitimate access when you step away from your device. After of inactivity, your session ends and you will must log in again. If you have activated the “remember me” option, you will be logged back in automatically when you come back, as long as your session expired due to inactivity rather than a manual logout. We chose the window following research demonstrating that it balances security with ease for the typical Polish player session length.
Are my login information shared with third parties?
We never share your login credentials with any outside entity. We store only a cryptographically salted hash of your password, which is computationally irreversible. Your email address is used exclusively for account-related messages and is never sold or shared with marketing partners without your explicit consent. Our identity verification documents are held in an encrypted archive separate from your gaming account data and are available only to our compliance team, which operates under rigorous data protection measures aligned with Polish and European Union regulations.
Grasping the mechanisms behind a casino login interface transforms it from a mundane obstacle into a meticulously designed gateway that protects both the player and the platform. spojrzenie od środka All decisions we make, from the hashing algorithm that guards stored passwords to the phrasing of a Polish error message, strikes a balance between security needs and the basic need to allow real players into their accounts without unnecessary friction. The next time we type our email address into a login form at SpinMaya Casino, we can understand that the seconds spent waiting to log in are filled with cryptographic handshakes, risk assessments, and integrity checks that operate quietly for our benefit. A carefully built login experience remains inconspicuous, and that unobtrusiveness is the ultimate accolade for a security system.